Security · API
Password Strength API
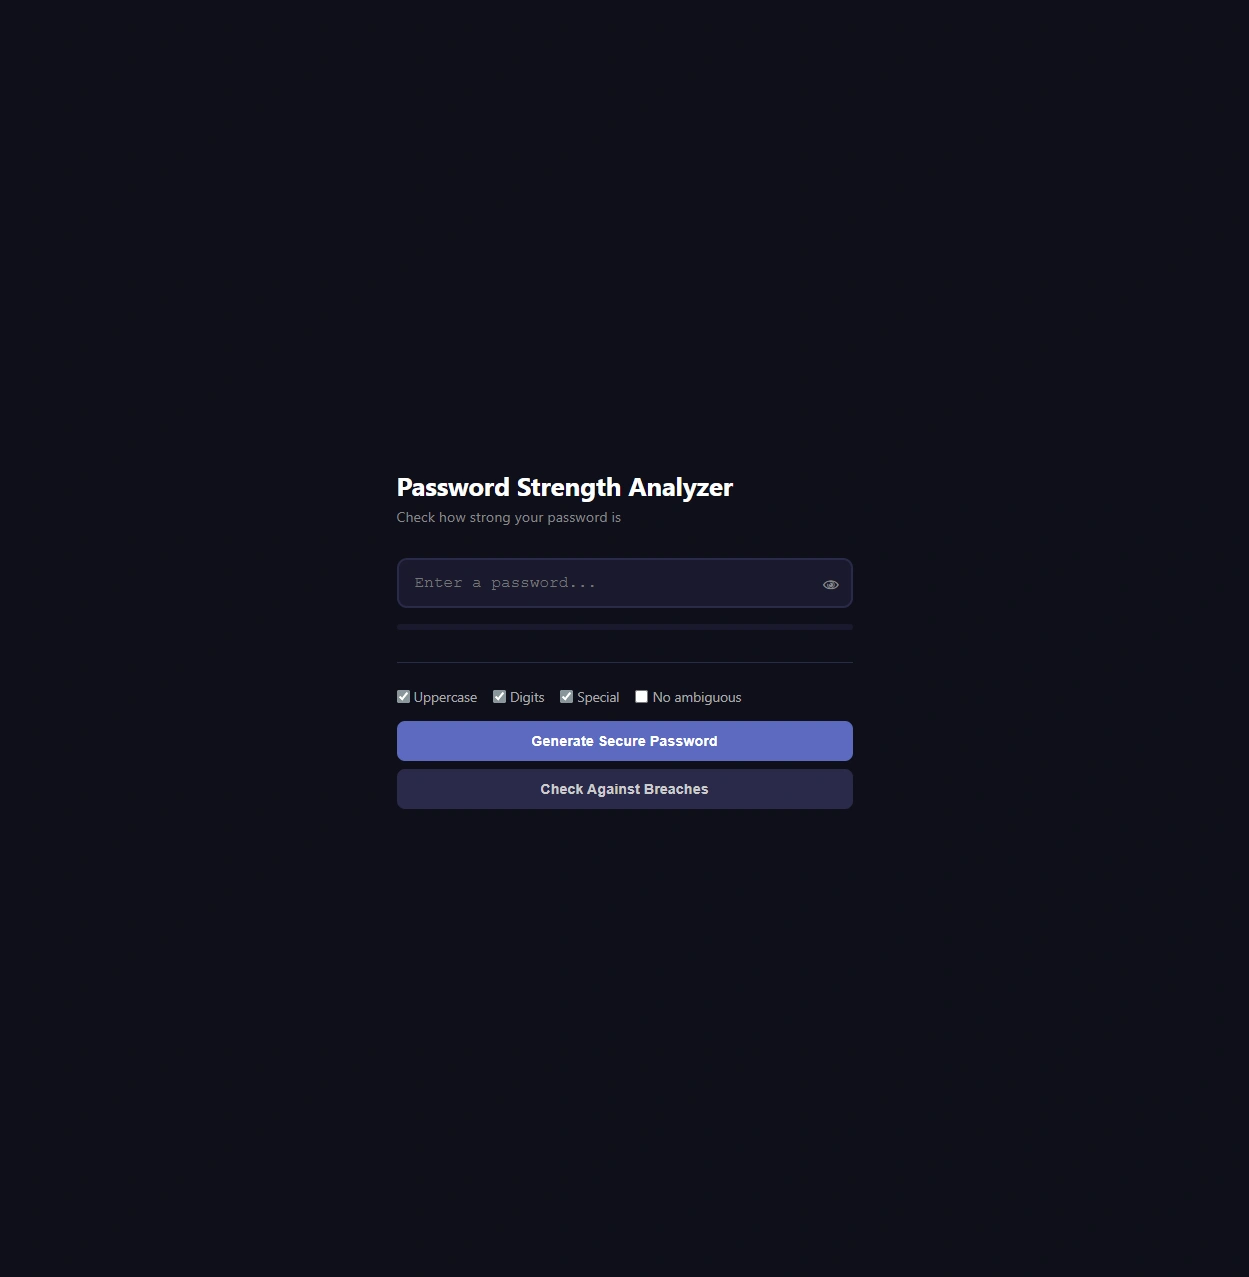
A password analysis API that returns entropy, breach status and crack-time estimates, using partial-hash lookups with Have I Been Pwned.
The challenge.
Password strength feedback needs to account for common patterns and known breaches, alongside entropy and crack-time estimates.
The approach.
A FastAPI microservice with entropy scoring, pattern detection and Have I Been Pwned k-anonymity breach checks. The API receives the submitted password and computes its SHA-1 hash; only the first five hash characters are sent to the external breach service.
Engineering decisions.
-
HIBP k-anonymity lookup sends only a SHA-1 prefix to Have I Been Pwned; the FastAPI service still receives the submitted password.
-
Entropy scoring plus pattern detection for a meaningful strength signal.
-
Documented FastAPI endpoints, packaged with Docker.
The outcome.
Returns entropy, breach status and crack-time estimates through documented API endpoints for integration into authentication workflows.